How AWS Uses X.509 PKI to Secure AI Agent Identity
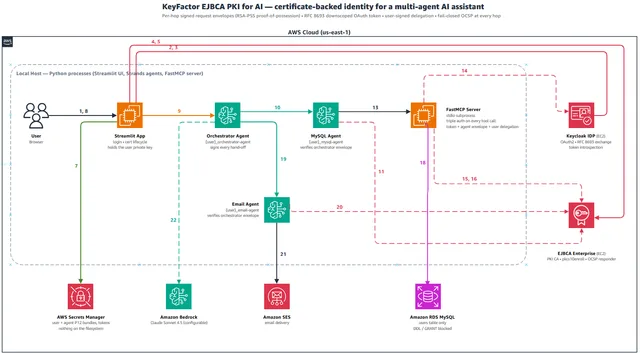
AWS and Keyfactor jointly released a reference architecture that uses Keyfactor EJBCA's X.509 PKI to establish verifiable, revocable cryptographic identities for AI agents, filling the gap left by MCP's lack of a built-in authentication standard. The solution combines Amazon Bedrock, the AWS Strands Agents SDK, AWS Secrets Manager, and Amazon RDS, and covers three trust boundaries—user authentication, agent-to-agent communication, and MCP tool invocation—through four layers of mechanisms: signed request envelopes, user-signed delegation assertions, RFC 8693 audience-restricted tokens, and real-time OCSP revocation checks.
AWS and Keyfactor jointly released a reference architecture that uses Keyfactor EJBCA's X.509 PKI to establish verifiable, revocable cryptographic identities for AI agents, filling the gap left by MCP's lack of a built-in authentication standard. The solution combines Amazon Bedrock, the AWS Strands Agents SDK, AWS Secrets Manager, and Amazon RDS, and covers three trust boundaries—user authentication, agent-to-agent communication, and MCP tool invocation—through four layers of mechanisms: signed
Matched fieldsBody